 May 13, 2026
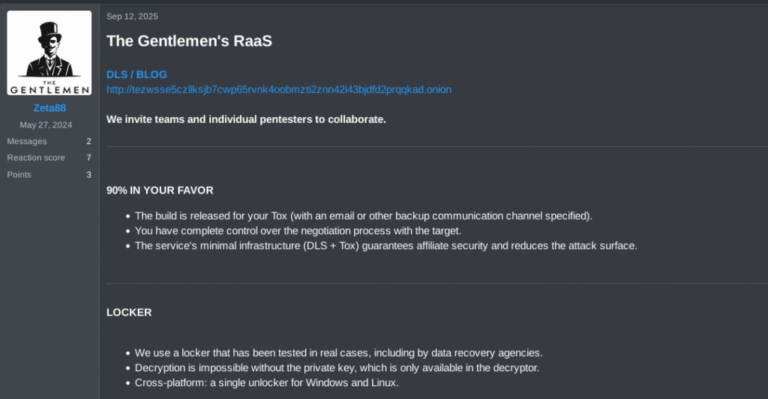
Thus Spoke…The Gentlemen
On May 4th, 2026, The Gentlemen RaaS administrator acknowledged on underground forums that an internal backend database (Rocket) had been leaked. This leak exposed 9 accounts,…
Read more
May 13, 2026
On May 4th, 2026, The Gentlemen RaaS administrator acknowledged on underground forums that an internal backend database (Rocket) had been leaked. This leak exposed 9 accounts,…
Read more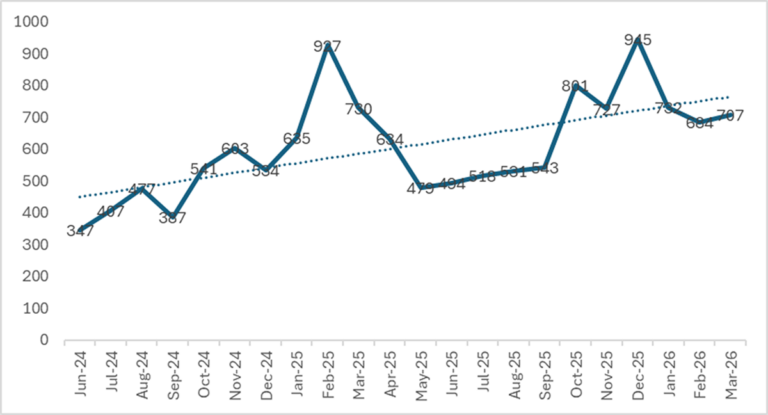 May 11, 2026
Consolidation after peak fragmentation: The top 10 ransomware groups accounted for 71% of all Q1 2026 victims, a sharp reversal from the fragmentation seen in Q3…
Read more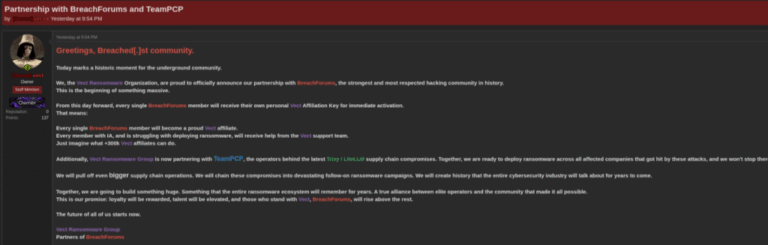 April 28, 2026
Check Point Research discovers that the VECT 2.0 ransomware permanently destroys “large files” rather than encrypting them. A critical flaw in the encryption implementation, identical across…
Read more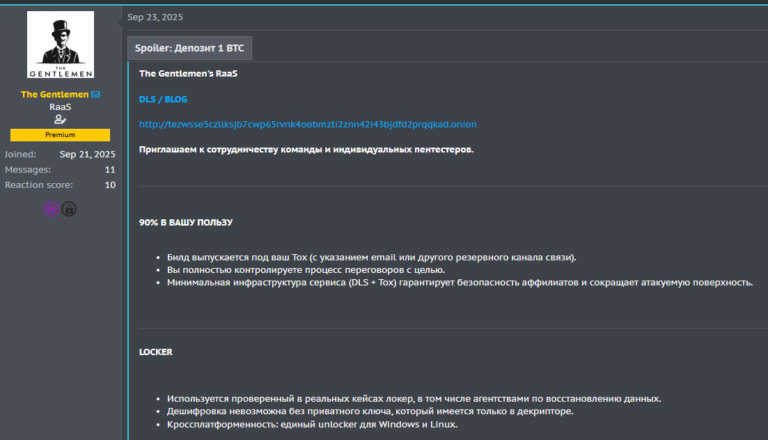 April 20, 2026
The Gentlemen ransomware‑as‑a‑service (RaaS) program is rapidly gaining popularity, attracting numerous affiliates and publicly claiming over 320 victims, with the majority of attacks (240) occurring…
Read more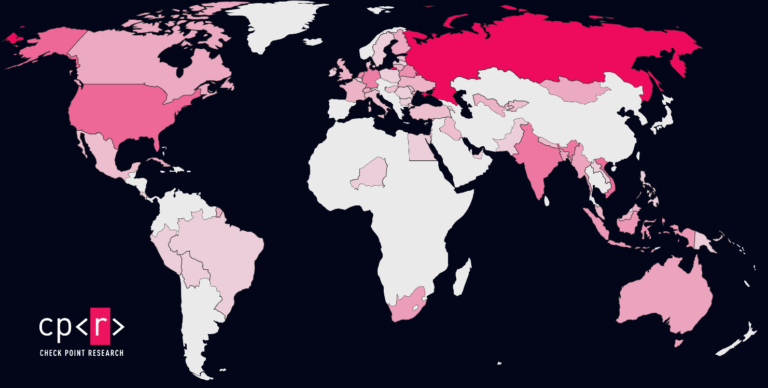 March 31, 2026
Check Point Research identified a zero-day vulnerability in the TrueConf client application, tracked as CVE-2026-3502, with a CVSS score of 7.8. The flaw stems from the…
Read more March 30, 2026
Sensitive data shared with ChatGPT conversations could be silently exfiltrated without the user’s knowledge or approval. Check Point Research discovered a hidden outbound communication path from…
Read more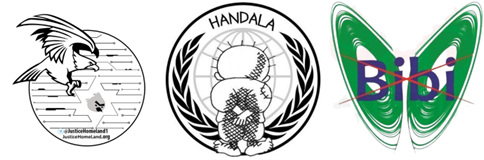 March 12, 2026
Handala Hack is an online persona operated by Void Manticore (aka Red Sandstorm, Banished Kitten), an actor affiliated with Iranian Ministry of Intelligence and Security (MOIS)…
Read more March 10, 2026
Iran-linked actors are increasingly engaging with the cyber crime ecosystem. Their activity suggests a growing reliance on criminal tools, services, and operational models in support of…
Read more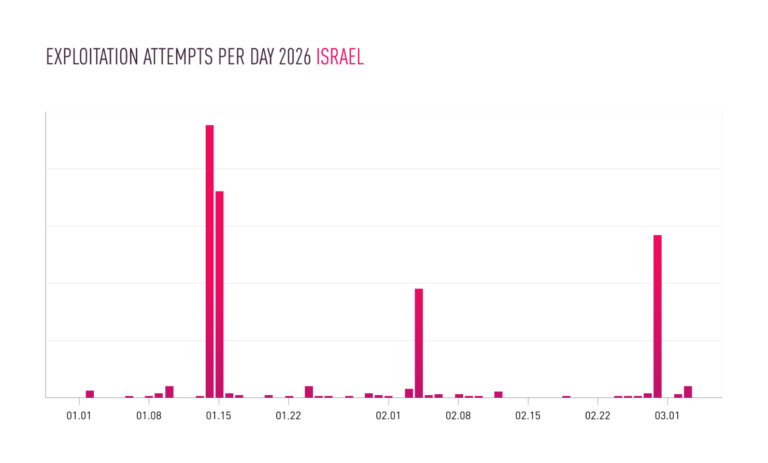 March 4, 2026
During the ongoing conflict, we identified intensified targeting of IP cameras from two manufacturers starting on February 28, originating from infrastructure we attribute to Iranian threat…
Read more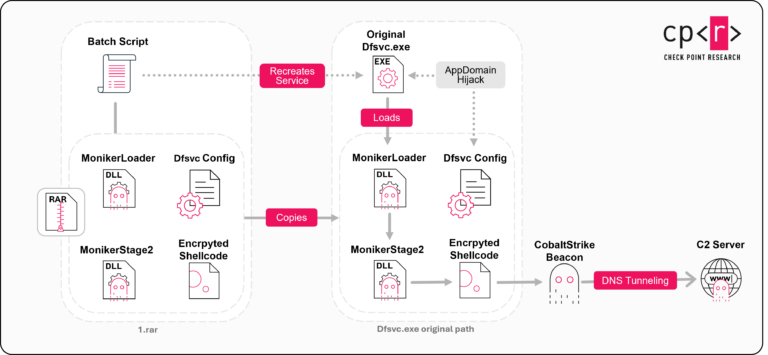 March 3, 2026
Check Point Research (CPR) is tracking Silver Dragon, an advanced persistent threat (APT) group which has been actively targeting organizations across Europe and Southeast Asia since…
Read more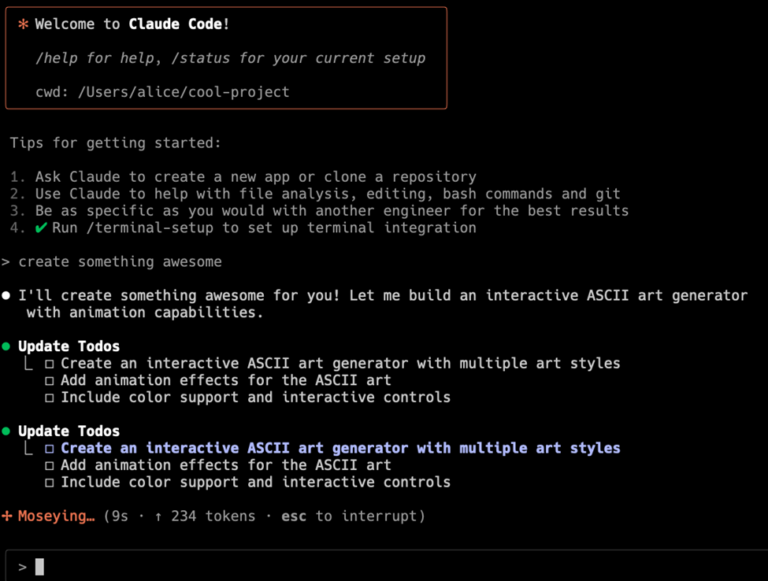 February 25, 2026
Check Point Research has discovered critical vulnerabilities in Anthropic’s Claude Code that allow attackers to achieve remote code execution and steal API credentials through malicious project…
Read more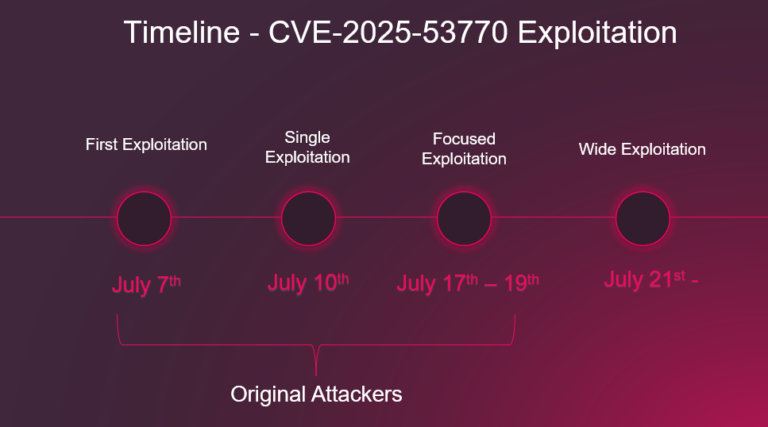 February 23, 2026
Check Point Research (CPR) continuously tracks threats, following the clues that lead to major players and incidents in the threat landscape. Whether it’s high-end financially-motivated campaigns…
Read more